A Significant Data Fiduciary (SDF) is an entity designated by the Central Government under Section 10(1) of the Digital Personal Data Protection Act, 2023 (DPDP Act). It carries an intensified tier of statutory data governance obligations.
For an Indian bank or non-banking financial company (NBFC), designation as an SDF is widely expected given the scale and sensitivity of financial records. As of September 2026, however, the Central Government has not published an official notification designating specific entities or classes of entities as SDFs.
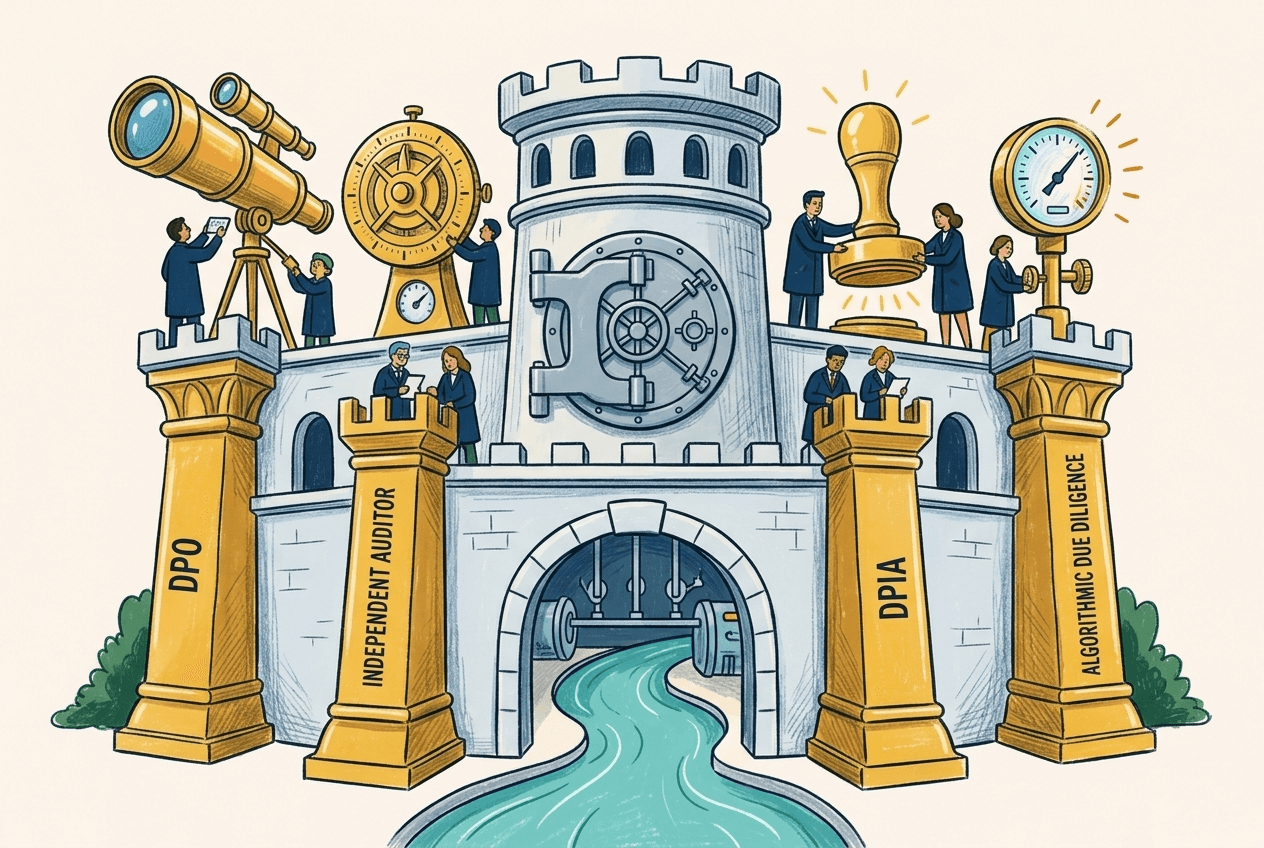
Section 10 and Rule 13 of the Digital Personal Data Protection Rules, 2025 come into force under the eighteen-month commencement schedule. They will then require an SDF to:
- Appoint an India-based Data Protection Officer responsible to the Board.
- Engage an independent data auditor.
- Conduct annual Data Protection Impact Assessments.
- Perform due diligence on algorithmic software.
The foundational principles of the law, baseline fiduciary obligations, and enforcement timelines are set out on the sibling pages: What Is the DPDP Act?, What Is a Data Fiduciary Under India’s DPDP Act?, and The DPDP Compliance Timeline: When the DPDP Rules 2025 and the DPDP Act Commence for Banks and NBFCs.
This guide focuses on three things:
- The SDF classification.
- The statutory designation criteria.
- The operational gap between existing Reserve Bank of India (RBI) controls and the new DPDP mandates.
How an Entity Gets Designated as a Significant Data Fiduciary
The seven assessment factors under Section 10(1)
Under Section 2(z) of the DPDP Act, a Significant Data Fiduciary is any Data Fiduciary or class of Data Fiduciaries designated as such by the Central Government under Section 10. The statute sets no fixed numeric thresholds.
Instead, Section 10(1) lets the Central Government notify an entity or a class of entities based on seven statutory factors:
- Volume and sensitivity of personal data processed (Section 10(1)(a)): The scale of customer records and whether they involve sensitive categories such as financial records, biometric data, or identity documents.
- Risk of harm to the Data Principal (Section 10(1)(b)): The potential for financial loss, identity theft, unauthorized profiling, or distress if personal data is breached or misused.
- Potential impact on the sovereignty and integrity of India (Section 10(1)(c)): Exposure that could affect national security or strategic interests.
- Risk to electoral democracy (Section 10(1)(d)): The potential for mass voter profiling, manipulation, or micro-targeting.
- Security of the State (Section 10(1)(e)): Vulnerabilities in critical national infrastructure or core communication systems.
- Public order (Section 10(1)(f)): The risk of systemic disruption, fraud-driven runs, or civil unrest.
- Such other factors as may be considered necessary (Section 10(1)(g)): Residual discretion reserved for the Central Government.
Neither the DPDP Act, 2023 nor the DPDP Rules, 2025 published under G.S.R. 846(E) sets quantitative metrics, such as registered customer volume or transaction turnover. Designation remains an executive determination issued by official gazette notification.
The Four Mandatory Obligations of an SDF
Statutory additions beyond baseline Section 8 duties
Designation as an SDF does not replace baseline Data Fiduciary duties under Section 8. Instead, Section 10(2) of the Act and Rule 13 of the DPDP Rules, 2025 superimpose four additional statutory obligations:
1. Appointment of a Data Protection Officer (Section 10(2)(a))
An SDF must appoint a Data Protection Officer (DPO) who meets three statutory requirements. The DPO must:
- Be an individual based in India.
- Be responsible directly to the Board of Directors or similar governing body.
- Act as the point of contact for the grievance redressal mechanism established under the Act.
2. Appointment of an Independent Data Auditor (Section 10(2)(b))
An SDF must appoint an independent data auditor to evaluate its compliance with the provisions of the DPDP Act and Rules. The auditor conducts an external, objective examination of data management practices, processing lifecycles, and technical safeguards.
3. Periodic DPIA and Annual Data Audits (Section 10(2)(c) & Rules 13(1)-(2))
Under Rule 13(1) and Rule 13(2) of the DPDP Rules, 2025, an SDF must:
- Undertake a Data Protection Impact Assessment (DPIA) once in every period of 12 months from the date of notification as an SDF.
- Undertake a data audit once in every 12 months.
- Furnish a report of significant observations from the audit and DPIA directly to its Board of Directors.
4. Algorithmic Software Due Diligence & Cross-Border Conditions (Rules 13(3)-(4))
Rule 13(3) introduces a technical governance requirement. The SDF must do due diligence to verify that technical measures, including algorithmic software it adopts, are not likely to pose a risk to the rights of Data Principals.
In addition, under Rule 13(4), an SDF must make sure that certain data is not transferred outside India. This covers personal data and traffic data specified by the Central Government on the recommendation of an expert committee.
Commencement Status and Enforcement Schedule
The eighteen-month timeline for Section 10 and Rule 13
The additional obligations under Section 10 and Rule 13 are not yet in force as of September 2026.
Under Commencement Notification G.S.R. 843(E) dated 13 November 2025, Section 10 of the DPDP Act commences in the eighteen-month tranche. Rule 1 of the DPDP Rules, 2025 (G.S.R. 846(E)) sets an identical eighteen-month trigger for Rule 13.
The computed date depends on the start day:
- Calculated from the 13 November 2025 gazette publication date: 13 May 2027.
- Calculated from 14 November 2025: 14 May 2027.
Neither instrument prints a calendar date. Both express the deadline as an elapsed period running from gazette publication.
| Provision | Obligation | Commencement Status | Enforcement Tranche (computed as 13 May 2027) |
|---|---|---|---|
| Section 10(1) | Central Government power to notify SDFs. | Not yet in force. | Eighteen-month tranche (computed as 13 May 2027) |
| Section 10(2)(a) | Mandatory India-based DPO reporting to Board. | Not yet in force. | Eighteen-month tranche (computed as 13 May 2027) |
| Section 10(2)(b) | Appointment of Independent Data Auditor. | Not yet in force. | Eighteen-month tranche (computed as 13 May 2027) |
| Section 10(2)(c) & Rule 13(1)-(2) | Annual DPIA and statutory data audit. | Not yet in force. | Eighteen-month tranche (computed as 13 May 2027) |
| Rule 13(3) | Due diligence on algorithmic software. | Not yet in force. | Eighteen-month tranche (computed as 13 May 2027) |
| Rule 13(4) | Cross-border transfer restrictions on specified data. | Not yet in force. | Eighteen-month tranche (computed as 13 May 2027) |
What Changes for a Bank or NBFC: RBI Controls vs. DPDP Gap Analysis
Comparing prudential banking guidelines with statutory privacy requirements
Scheduled commercial banks, large NBFCs, and financial market infrastructures already operate under rigorous prudential and operational directions from the Reserve Bank of India. These include the Master Direction on Information Technology Governance, Risk, Controls and Assurance Practices, 2023.
While existing banking controls satisfy technical cybersecurity hygiene, an SDF designation introduces distinct statutory duties that do not map directly onto current banking frameworks:
| Governance Domain | Existing RBI Framework | What DPDP Section 10 & Rule 13 Add | Operational Impact for BFSI |
|---|---|---|---|
| Executive Oversight. | Mandatory Chief Information Security Officer (CISO) overseeing information security and cyber resilience. | Section 10(2)(a) mandates an independent Data Protection Officer based in India reporting directly to the Board. | The DPO role cannot simply be added as a secondary duty to the CISO or CIO without creating conflict of interest between security operations and privacy rights oversight. |
| Assurance & Audit. | Periodic Information System (IS) audits and RBI supervisory inspection. | Section 10(2)(b) and Rule 13(2) mandate an independent data auditor conducting an annual DPDP compliance audit. | Requires engaging a specialized privacy auditor evaluating compliance with statutory principles, consent records, and principal rights, distinct from standard IS audits. |
| Risk Assessment. | Operational risk assessments, vulnerability assessments, and penetration testing (VAPT) | Rule 13(1) mandates a formal Data Protection Impact Assessment (DPIA) completed once every 12 months. | Requires structured evaluations of processing risks, data flow mapping, and harm assessments submitted to the Board. |
| Model & Algorithm Governance. | Guidelines on Digital Lending requiring algorithmic transparency and disclosure of underwriting factors | Rule 13(3) mandates statutory due diligence to verify that algorithmic software is not likely to pose a risk to the rights of Data Principals. | Extends beyond credit underwriting to encompass all automated models, including fraud detection, transaction monitoring, and biometric identity verification. |
| Data Localization. | RBI IT Outsourcing Directions requiring local storage of banking and payment data. | Rule 13(4) restricts cross-border transfer of specific personal and traffic data notified on expert committee recommendation. | Adds potential restrictions on outbound processing flows for fraud intelligence, cloud analytics, and group-wide risk aggregations. |
The Algorithmic Due Diligence Mandate (Rule 13(3))
Extending compliance into automated models, scoring engines, and KYC pipelines
For digital lenders, retail banks, and fintechs, Rule 13(3) represents the most significant operational expansion of compliance scope. BFSI institutions rely heavily on automated systems across their operational lifecycle:
- Automated credit scoring and loan origination engines.
- Machine learning models for real-time transaction monitoring and fraud detection.
- Alternative data analysis for customer underwriting and risk profiling.
- Biometric matching and liveness verification systems in digital KYC.
Under the Guidelines on Digital Lending issued by the RBI, lenders must disclose key underwriting parameters to borrowers upon request. However, Rule 13(3) establishes an affirmative obligation to conduct technical due diligence ensuring algorithms do not pose risks to Data Principal rights. This requires compliance teams to document:
- Training data lineage and bias evaluations: Ensuring training sets do not embed discriminatory underwriting or credit denial factors.
- Model explainability frameworks: Enabling customer grievance redressal when automated systems impact individuals.
- Vendor risk assessments: Auditing third-party scoring algorithms and identity models embedded in customer onboarding pipelines.
Statutory Penalties for Non-Compliance
The ₹150 crore statutory ceiling under Item 4 of the Schedule
Penalties for non-compliance under the DPDP Act are determined by the Data Protection Board of India under Section 33. The statute specifies statutory ceilings rather than fixed or per-instance penalties:
- Under Item 4 of the Schedule to the DPDP Act, 2023, a breach of the additional Significant Data Fiduciary obligations under Section 10 carries a penalty ceiling of up to ₹150 crore.
- In assessing quantum, Section 33 requires the Board to weigh statutory factors. These include the nature, gravity, and duration of the breach, the number of affected Data Principals, repetitive conduct, and any mitigating action undertaken by the entity.
What This Designation Framework Means for BFSI Compliance Planning
Governance separation, vendor risk, and board accountability
The observations below represent this piece’s analysis of the statutory framework and regulatory texts cited above. While the statutory provisions carry legal force once commenced, the operational deductions drawn here are analytical.
“Treating the DPO mandate as a title re-assignment for an existing CISO or legal counsel creates immediate governance friction. Separating data privacy governance from technical security administration prevents internal conflicts of interest.”
DPO and CISO should be separate roles
On this piece’s reading, treating the DPO mandate as a title re-assignment for an existing CISO or legal counsel creates immediate governance friction.
- Under Section 10(2)(a), the DPO must report directly to the Board of Directors and act as the neutral point of contact for Data Principal grievances.
- A CISO, in contrast, is an operational executive. The CISO is tasked with network defense, system availability, and IT operations under the Master Direction on Information Technology Governance, Risk, Controls and Assurance Practices, 2023.
Combining these roles risks an operational conflict of interest. The same individual would evaluate data minimization and processing lawfulness, and would also be responsible for the uptime of data-consuming infrastructure.
Vendor models are now a Board-level risk
Rule 13(3) effectively shifts algorithmic governance from an internal IT testing convention into an audited statutory obligation. Banks and NBFCs often source fraud-scoring models, alternative scoring engines, and KYC verification pipelines from external RegTech and fintech vendors.
Financial institutions will therefore have to ask their technology partners for model auditability and risk assessments. Under Section 8(1), a Data Fiduciary remains liable for compliance regardless of any outsourcing contract. Third-party algorithmic verification is therefore a critical priority for Board risk committees.
Frequently Asked Questions
Key answers regarding Significant Data Fiduciary designation, timelines, and roles
This article is for informational purposes only and does not constitute legal, regulatory, or compliance advice. Regulated entities should seek formal advice from qualified legal counsel regarding their specific statutory obligations under the DPDP Act and RBI regulations.
Sourcing notes for this piece: statutory provisions of the DPDP Act, 2023 are cited from the Gazette of India Extraordinary text. The DPDP Rules, 2025 and Commencement Notification G.S.R. 843(E) are cited from published MeitY notifications. Banking framework comparisons are drawn from extant Reserve Bank of India Master Directions.
Bhanujeet Choudhary
Head of Compliance, KYCKART
Assess your Significant Data Fiduciary readiness
KYCKART assists banks, NBFCs, and financial platforms in auditing algorithmic workflows, identity verification lifecycles, and DPDP readiness.
Consult with our compliance specialistsarrow_forward