The Multi-Hop Mule Dilemma: Why Institutional Silos Blind Fraud Detection
Digital payment fraud outpaces single bank controls. In UPI and net banking scams, fraudsters move stolen funds across chains of mule account networks in minutes.
Bank monitoring tools work only within internal borders. When funds leave, the sending bank sees an outflow. The next bank sees an inflow and quick withdrawal. Neither bank sees the full money trail. Disrupting these multi-hop chains needs joint action.
Yet Indian banks cannot simply swap customer records. Lenders face strict confidentiality duties and real business risks:
- Customer privacy rules: Section 6 of the Digital Personal Data Protection Act, 2023 requires valid, purpose-specific consent to process digital personal data. Banks cannot pool, move, or disclose user transaction logs to peer firms without explicit statutory authority or clear user consent. Section 8 also mandates strong technical safeguards against data exposure.
- Data sharing limits: Standard tools like REST APIs, Model Context Protocol servers, and vanilla agent frameworks pass plaintext data across trust borders.
- The collaboration gap: An academic survey on privacy technologies for financial intelligence shows that data silos are the primary technical barrier in stopping financial crime. International policy studies by the Financial Stability Board also show that interbank systems need privacy-enhancing tools to balance crime checks with data rights.
Enter AP3: Shifting from Raw Data Exchange to Governed Execution
Governed execution allows autonomous agents to query peer risk models without exchanging raw identifiers.
A research paper at the Global Fintech Fest (GFF) 2026 shows a path past this dilemma. In a compendium titled Trustworthy Agentic AI: Defining Next-Generation Governance from IIIT Bangalore's Centre for Information Technology and Public Policy, researchers from Silence Laboratories proposed the Agent Privacy-Preserving Protocol. The compendium features forewords from Sahil Kini, CEO of the Reserve Bank Innovation Hub, and Dr. Debabrata Das, Director of IIIT Bangalore.
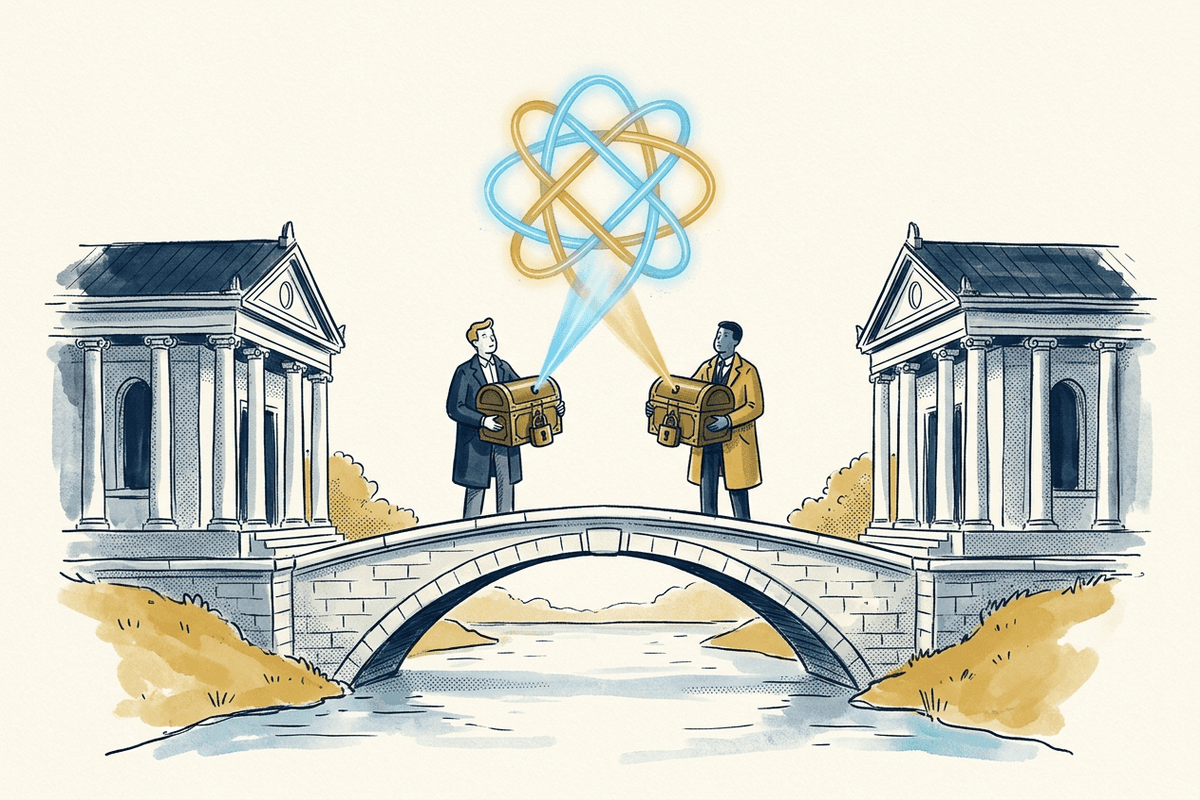
AP3 changes how automated agents work together. Instead of moving sensitive data across bank borders, AP3 sets up governed execution. Independent systems compute risk scores over encrypted or split inputs. Plain customer data never leaves the home bank.
AP3 extends the open-source Agent2Agent protocol, enabling software agents to advertise and run cryptographic operations across standard network transports.
The protocol runs on Silence Laboratories' Cryptographic Computing Virtual Machine and is open-sourced under Linux Foundation Decentralized Trust Labs. Running math over encrypted inputs removes the need to store banking records in central targets.
The Three Cryptographic Building Blocks of AP3
SMPC, hardware enclaves, and threshold signing working together to protect customer records.
The protocol blends three privacy tools to enable joint fraud checks without data leaks, as documented in the AP3 architecture specification:
SMPC allows two or more systems to compute a joint output over private inputs. Neither bank reveals plaintext records. Its primary tool is Private Set Intersection (PSI), matching suspicious accounts without disclosing non-matching lists.
For complex scoring models, code runs inside a secure chip. Trusted Execution Environment (TEE) attestation creates a hardware-signed proof confirming scoring algorithms ran without tampering or outside inspection.
Instead of static API keys, AP3 ties agent actions to cryptographic keys held across multiple parties. An agent cannot act without multi-party approval, ensuring tamper-proof audit trails.
Academic research on collaborative anti-money laundering shows that privacy-preserving methods expose complex layering rings. Graph analytics studies by TigerGraph confirm that spotting layering needs pattern links across banks. Combining SMPC, secure chips, and threshold keys lets banks run collaborative graph analytics without exposing customer accounts.
Architectural Workflow: How an Interbank Fraud Check Runs
The 9-step operational sequence of an AP3 cross-bank fraud verification session.
The requesting bank transmits a signed PrivacyIntentDirective scoping the query, runs cryptographic rounds over standard network transports, and commits a signed PrivacyResultDirective receipt to local compliance logs.
Cross-Bank Collaborative Fraud Signal Verification Workflow (AP3)
Bank A detects rapid velocity anomalies on an outgoing transfer directed toward Bank B.
Bank A agent queries Bank B agent card to identify supported cryptographic privacy extensions.
Bank B advertises signed dataset metadata without disclosing underlying customer records.
Bank A transmits a signed PrivacyIntentDirective specifying purpose and bounded query limits.
Agents execute private set intersection over encrypted hashes using secure multi-party computation.
Enclave generates a verifiable hardware attestation confirming unmodified algorithm execution.
Bank A receives a minimal boolean flag or bounded risk score without raw account details.
Both agents store signed PrivacyResultDirective receipts in internal compliance logs.
Bank A risk engine places a temporary hold on the transaction pending verification.
Note: Step 09 illustrates an operational workflow for bank risk engines, not a protocol mandate. When a check returns a positive match, the sending bank can hold the transfer while keeping customer records safe.
Cryptographic Sharing vs. Centralized DPIP Registry
Contrasting peer-to-peer compute with the RBI's upcoming centralized fraud repository.
India is also testing central defenses. On June 7, 2024, the Reserve Bank of India issued a statement on developmental and regulatory policies proposing the Digital Payments Intelligence Platform (DPIP).
The Reserve Bank formed a committee led by Shri A.P. Hota, former MD and CEO of NPCI, to guide the plan. Prototype work continues through the Reserve Bank Innovation Hub toward the Indian Digital Payment Intelligence Corporation. As detailed in our guide to DPIP and central fraud registries, DPIP aggregates suspicious accounts into a central smart registry for ecosystem querying.
AP3 and DPIP reflect fundamentally different design choices:
| Feature | AP3 Cryptographic Model | RBI DPIP Model | Raw Data Sharing (REST / MCP) |
|---|---|---|---|
| Network Shape | Peer-to-peer compute across banks | Central consortium registry | Direct point-to-point links |
| Data Location | Data stays on premise; only encrypted math moves | Fraud flags pooled into central registry | Plain customer records cross borders |
| DPDP Act Fit | High: built-in data minimisation and purpose limits | Needs central legal mandate or public utility rules | Low: high friction under Section 6 consent rules |
| Trust Base | Math checks via SMPC and secure hardware enclaves | Trust in central registry operator and governance | Direct contract trust between counterparty banks |
| Main Role | Real-time pre-transfer checks for fast mule rings | Ecosystem-wide blacklists and retroactive flags | Bilateral file swaps and account servicing |
Cryptographic signal sharing replaces the forced trade between data privacy and fraud visibility by moving code to the data rather than pooling data in a central hub.
What This Means for Indian Banks and Fintechs
Practical implications and boundaries for risk and engineering leadership.
Read together, the technical tests of AP3 and the policy path of DPIP point to clear lessons for Indian banks. India will likely build a two-tier fraud defense rather than rely on one platform: central registries like DPIP track known bad actors across the country, while peer-to-peer tools like AP3 solve immediate pre-transaction checks where abnormal velocity is detected.
AP3 relies partly on secure enclave chips. Indian banks run varied server hardware across private clouds and on-premise centers, where enclave support is not uniform.
Indian courts and supervisory bodies under Bharatiya Sakshya Adhiniyam, 2023 have not issued formal rules on multi-party cryptographic receipts. Treat outputs as risk signals, not legal evidence.
AP3 remains an open specification in research preview. Banks can test prototypes, but live interbank deployment requires shared industry standards.
KYCKART provides unified identity verification, KYC onboarding, and fraud checks for individual institutions. KYCKART does not operate interbank multi-party cryptographic networks. This review shares insights from GFF 2026 to help risk teams evaluate privacy-preserving fraud controls.
Cross-Bank Fraud Signal Sharing & Privacy Protocols
Disclaimer: This article provides regulatory, industry, and technical architecture analysis for educational purposes only. It does not constitute legal, regulatory, tax, or compliance advice. Institutions should consult qualified legal or compliance counsel before operationalizing interbank signal-sharing or cross-boundary data workflows.