
Bank Account Verification: Comparing Penny Drop, Account Aggregator and API-Based Methods
Compare bank account verification methods in India: penny drop micro-deposits, Account Aggregator consent flows, and direct API checks. What each validates, where each fits, and their fraud limitations.
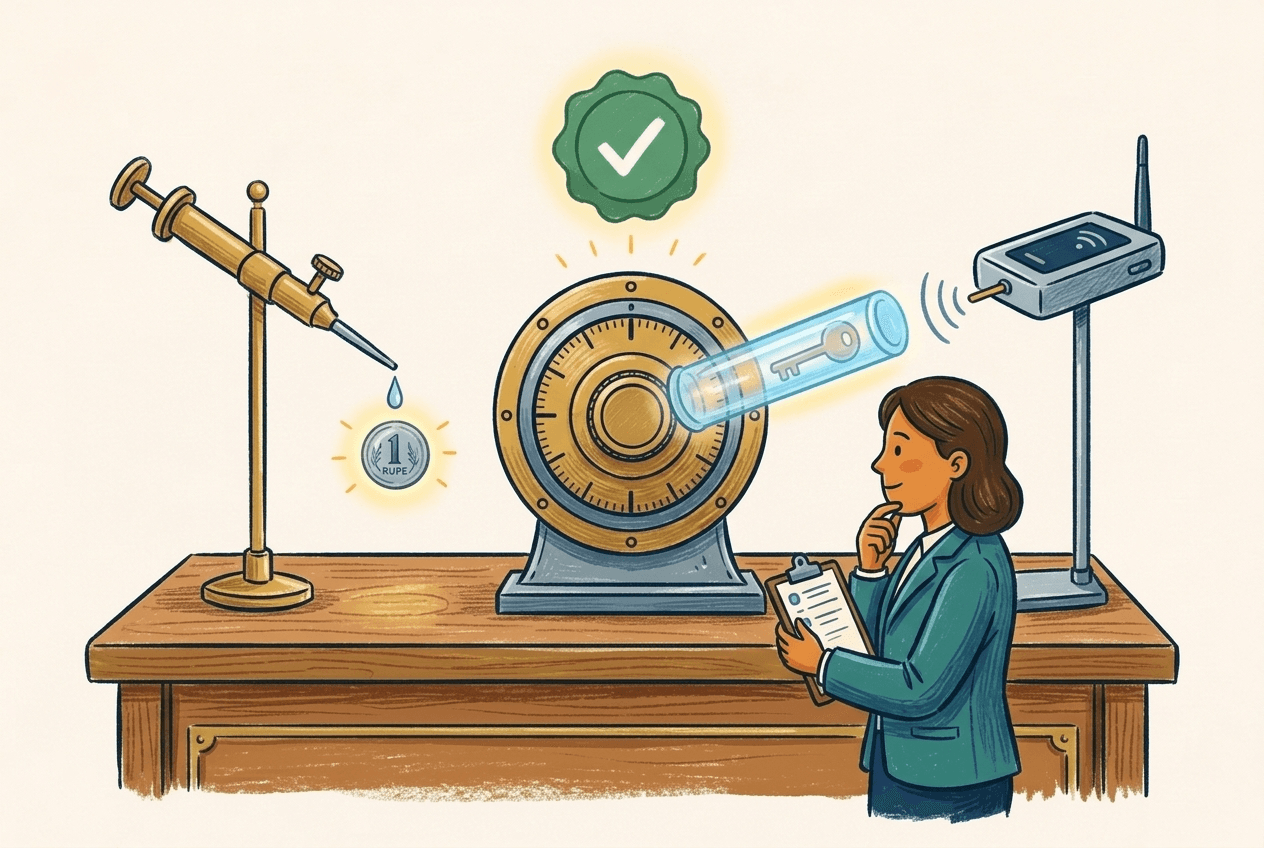
Bank account verification is an automated operational procedure used by banks, NBFCs, fintech lenders, and payment platforms to confirm that a customer’s bank account exists, is active, and is legally registered in the applicant’s name before money moves. In Indian BFSI onboarding, institutions primarily choose between three distinct mechanisms: penny drop micro-deposits that credit Re 1 to test account rails, Account Aggregator consent flows that fetch verified account profiles directly from source banks without money transfer, and direct API or Reverse Penny Drop checks that capture verified details over payment networks like UPI. Choosing the right method depends on whether an institution needs instant single-point ownership confirmation, frictionless user onboarding, or comprehensive financial analysis.
Why Bank Account Verification Matters in BFSI Onboarding
In digital lending, merchant onboarding, and wealth management, verifying bank account ownership is a core risk control. When an institution disburses a loan or issues an investor payout, routing funds to an unverified or incorrectly entered account leads to costly recovery cycles, customer disputes, and regulatory scrutiny. Automated verification is routinely deployed by banks, NBFCs, fintech lenders, payment aggregators, and payroll platforms to ensure funds reach the intended beneficiary.
Beyond operational accuracy, verification confirms an account’s health. The process checks whether an account is active, dormant, frozen, or closed, and verifies the registered legal name in the bank’s records before setting up auto-debit mandates or releasing capital.
Indian financial regulators have explicitly embedded bank account verification into specific operational frameworks:
- 1.
Pension Fund Regulatory and Development Authority (PFRDA): Under Circular No. PFRDA/2023/29/Sup-CRA/09 dated October 25, 2023 (which modified Circular No. PFRDA/2021/21/SUP-NPST/2 dated July 20, 2021), PFRDA made penny drop verification with name matching mandatory for all National Pension System (NPS) exit and withdrawal requests, as well as for modifying subscriber bank account details.
- 2.
Securities and Exchange Board of India (SEBI): Under its Master Circular on KYC norms for the securities market (SEBI/HO/MIRSD/SECFATF/P/CIR/2023/169 dated October 12, 2023), consolidating its earlier digital-KYC circular of April 24, 2020, SEBI codified penny drop verification as a standard mechanism for validating bank details during online investor onboarding.
To understand how bank checks fit into broader onboarding requirements, see our guide on eKYC and digital KYC verification.
The Three Verification Methods Compared
Modern institutions operating in India evaluate three primary technical approaches for bank account verification. Each method uses different payment rails, delivers different depth of data, and introduces distinct user experience characteristics.
| Parameter | Penny Drop | Account Aggregator (AA) | Direct API / Reverse Penny Drop |
|---|---|---|---|
| Primary Mechanism | Business initiates Re 1 micro-deposit via IMPS, NEFT, or UPI | Encrypted consent-based data pull between FIP bank and FIU entity via licensed NBFC-AA | Customer initiates Re 1 transfer via UPI app to business VPA, or automated CBS query |
| User Input Required | Manual entry of Bank Account Number and IFSC Code | Mobile number and OTP to authenticate Account Aggregator consent handle | UPI pin authorization on mobile UPI app, zero manual account/IFSC typing |
| Funds Transferred | Re 1 sent from business to customer account | None (zero monetary movement) | Re 1 sent from customer, typically refunded automatically |
| Data Returned | Account status (active/dormant/frozen) and CBS registered name | Authenticated account profile, operational status, and historical transaction statements | Account number, IFSC, registered account name from payment rail |
| Verification Latency | Near real-time (typically 2 to 10 seconds per API call) | Consent-dependent (typically 15 to 30 seconds for OTP authentication) | Instantaneous upon UPI authorization (typically 2 to 5 seconds) |
| Common Failure Modes | Typing errors in account/IFSC, bank IMPS downtime, dormant or closed account | OTP delivery failure, customer consent drop-off, bank FIP server timeout | User abandons UPI app payment screen, UPI network timeout |
| Primary Regulatory Rail | NPCI / RBI payment rails (IMPS, NEFT, UPI) | RBI Master Direction on NBFC-Account Aggregators (2016) | NPCI UPI rail / RBI RTGS & NEFT Name Look-Up Facility (RBI/2024-25/99) |
Method 1: Penny drop micro-deposits
Penny drop verification remains the most established automated method in India. In this model, an enterprise verification engine initiates a Re 1 micro-deposit into the customer’s account via IMPS, NEFT, or UPI.
When the transaction processes, the receiving bank’s Core Banking Solution returns a confirmation payload containing two critical pieces of information: the account status (active, dormant, frozen, or closed) and the full registered beneficiary name. The verification engine then compares this returned name against the name submitted on the customer’s identity documents using fuzzy name-matching logic.
The limitation of traditional penny drop is user friction. The applicant must manually type their account number and IFSC code, which introduces data entry errors and drop-offs in mobile onboarding funnels. For a detailed breakdown of micro-deposit mechanics, see our standalone guide on penny drop verification.
Method 2: The Account Aggregator (AA) framework
The Account Aggregator framework provides a consent-driven alternative that bypasses payment rails entirely. Regulated under the RBI Master Direction - Non-Banking Financial Company - Account Aggregator (Reserve Bank) Directions, 2016 (DNBR.PD.054/03.10.119/2016-17), this architecture enables secure, digital data sharing across regulated financial entities.
Within this ecosystem, RBI-licensed Account Aggregators operate as technical blind pipes. They transfer encrypted financial data from Financial Information Providers (such as commercial banks) to Financial Information Users (such as lenders or fintechs) without storing, decrypting, or viewing the underlying customer data.
Account Aggregator verification retrieves the customer’s authenticated account profile, operational status, and historical transaction statements directly from the bank. This happens with explicit, electronic, time-bound, and revocable customer consent authenticated through a mobile OTP. It involves zero monetary transfer and delivers verified statement data that supports both identity verification and credit underwriting.
Method 3: Direct APIs and Reverse Penny Drop
To overcome the manual typing friction of penny drop, providers developed Reverse Penny Drop (RPD). In this flow, the customer initiates a Re 1 payment from their preferred UPI app to a verified Virtual Payment Address (VPA) registered to the verifying enterprise.
When the customer completes the UPI transaction, the payment rail extracts the customer’s validated bank account number, IFSC code, and registered account holder name, transmitting them back to the business via webhook. The Re 1 payment is typically auto-refunded to the user. Because the customer never types an account number or IFSC, input errors are eliminated.
In parallel, central infrastructure is expanding direct query capabilities. On December 30, 2024, the Reserve Bank of India issued Circular RBI/2024-25/99 (DPSS.CO.RTGS.No.S959/04.04.016/2024-2025), directing all member banks participating in RTGS and NEFT to implement a recipient bank account name look-up facility by April 1, 2025. Developed with the National Payments Corporation of India (NPCI), this facility enables remitters to verify the beneficiary name in the destination Core Banking Solution before funds are sent, mirroring UPI’s look-up feature without moving any money.
What Bank Account Verification Confirms (and What It Doesn’t)
Deploying bank account verification effectively requires understanding both its capabilities and its boundaries.
Name matching: fuzzy scores and failure types
A bank verification API rarely receives an exact, character-for-character match with a customer’s submitted identity document. Variations occur due to expanded initials, dropped honorifics, married names, or minor clerical errors.
To address this, verification platforms deploy fuzzy name-matching algorithms like Levenshtein distance, Jaro-Winkler, and token-based phonetic comparisons. These algorithms evaluate the textual similarity between the name on file with the bank and the name on the customer’s PAN or Aadhaar card, generating a similarity score from 0 to 100. If the score falls below the institution’s preset risk threshold, the result is flagged as a name mismatch requiring secondary document review.
Institutions must distinguish between two distinct failure categories:
- •Invalid result: Signals a structural banking failure. The account number or IFSC does not exist, or the receiving bank has flagged the account as closed, dormant, or restricted. No funds can move (Cashfree).
- •Mismatch result: Confirms the account is valid and operational, but the legal name registered with the destination bank Core Banking Solution conflicts with the applicant’s stated identity (HyperVerge).
The Fraud Boundary: Mule Accounts and Point-in-Time Limits
The most critical operational blind spot in bank account verification is assuming that a verified account is safe from fraud.
Bank account verification confirms account existence and registered ownership at a single point in time. It does not measure creditworthiness, financial solvency, or transaction velocity, and it cannot determine whether an account is operating as a money mule account on its own.
In a mule account scheme, the account is real, active, and legally opened in the name of an individual who has either rented out their credentials or been deceived by a syndicate. When a verification check is performed, the account returns an active status and the registered name matches the submitted KYC document perfectly.
Furthermore, fraud rings actively exploit automated verification tools. Syndicates frequently run penny drop micro-deposits to test and validate stolen, purchased, or synthetic bank accounts, confirming that an account is receptive to incoming transfers before routing fraudulent loan proceeds or scam payouts into it. For a deeper examination of how organized networks operate, read our analysis on mule account fraud detection.
Addressing this exposure requires a defense-in-depth posture. Point-in-time account checks must be combined with continuous transaction monitoring, device fingerprinting, behavioral biometrics, and shared fraud databases like the Indian Cyber Crime Coordination Centre (I4C) Suspect Registry.
Where Each Verification Method Fits: a Decision Framework for BFSI
Read together, the technical capabilities and regulatory mandates of these three methods point to a clear operational division of labor across the BFSI lifecycle.
The practical implication is that no single bank verification method serves every stage of customer onboarding equally well. In lending workflows, Account Aggregator statement analysis delivers deep value upstream during credit underwriting, where evaluating cash flows, average balances, and repayment obligations is essential. However, deploying Account Aggregator rails purely to confirm an account number immediately prior to disbursal introduces unnecessary friction and potential drop-off.
Conversely, penny drop micro-deposits and Reverse Penny Drop excel downstream at the disbursement gate. They provide lightweight, instant confirmation that the destination account is currently operational and capable of receiving funds right before capital is wired.
This suggests that leading institutions should structure verification as an automated cascade:
- 1.
For mobile-first consumer onboarding: Route through Reverse Penny Drop as the primary option to eliminate manual account and IFSC entry errors, preserving high conversion rates (Setu).
- 2.
For fallback and institutional counterparties: Fall back to standard IMPS Penny Drop when a customer does not use UPI, or when onboarding corporate vendors where manual bank detail entry is standard practice (Cashfree).
- 3.
For credit-decisioned journeys: Deploy Account Aggregator rails upstream to bundle account ownership verification with financial statement retrieval, eliminating duplicate checks (Sahamati).
- 4.
For pre-disbursement risk defense: Combine point-in-time name matching with cross-institutional mule account screening to ensure verified accounts are not syndicate-controlled (Gridlines).
How KYCKART Helps
KYCKART integrates bank account verification into a unified fraud intelligence and onboarding architecture, connecting account status and name-matching results directly with document KYC, device telemetry, and institutional risk signals. By correlating bank account validation with real-time risk indicators, KYCKART helps banks, NBFCs, and fintechs prevent disbursement errors, detect suspicious account testing, and identify potential mule networks before funds leave the institution.
Frequently Asked Questions
Bhanujeet Choudhary
Head of Compliance, KYCKART
Published September 16, 2026
Disclaimer: This article provides operational and regulatory context for educational purposes and does not constitute legal, tax, or financial compliance advice.
KYCKART Intelligence
Verify Accounts and Catch Mule Networks in One Pass
KYCKART connects bank account validation and name matching to device telemetry and institutional risk signals, so a verified account still gets screened for mule activity before funds move.
See How KYCKART Verifies Onboarding Documentsarrow_forward